
Help firmware teams build on their last review.
FDIE connects firmware analysis with release history. We help teams understand component changes, retain vulnerability-review context and maintain technical evidence as their connected products evolve.
A new release should build on what you already know.
Connected products combine shared libraries, vendor SDKs and device-specific code across maintained releases. Each change creates a practical question: which earlier security decisions still apply?
FDIE brings component lineage, release comparisons and recorded assessment context into that review. Start with one product and two supported releases, then evaluate the evidence against your team’s existing workflow.
CRA preparation is one reason to maintain this history. Firmware analysis supports the technical work; product risk assessment, vulnerability handling and conformity remain the manufacturer’s responsibilities.
Understand component changes
Compare identified components and known relationships across analysed images, with coverage limits visible.
Retain useful review context
Bring earlier decisions into the next release review so analysts can judge what to reuse and what to investigate again.
Maintain technical evidence
Keep SBOM, VEX and supporting records available for release documentation and product assessments. See the CRA context and limits.
See the workspace behind FDIE.
The dashboard brings fleet findings, assessment history and compliance coverage into one starting point. Follow a summary into the underlying evidence and the decisions that need attention.

Four beliefs that shape everything we build.
Automate repeated analysis work
Use supported extraction, analysis and release comparisons in your workflow. Integration and coverage are scoped to the product; analysts retain the decisions.
Determinism over black-box AI
Every finding traces back to a rule, a CVE record, or a fact in the binary you can check yourself. No generative AI anywhere in the pipeline. Scan the same firmware twice with the same engine build and feed snapshot and get the same static findings; every report records which build and snapshot produced it.
Evidence supports product responsibility
Technical findings and control assessments support a broader product review. We keep unassessed controls visible and do not turn scanner output into a conformity claim.
Transparency builds trust. Obscurity does not.
We publish exactly what FDIE checks, how it scores, and what data it touches. A security tool that is a black box is not one we would trust either.
We built the disassembler. From scratch.
At the core of FDIE is FirmBin, our own binary analysis and disassembly engine, built from published ISA manuals rather than by wrapping Ghidra, Capstone or radare2.
It disassembles ELF, PE and raw images across 19 CPU architectures, including x86, ARM, ARM64, MIPS, RISC-V, PowerPC, SPARC, S390, MSP430, TriCore, PIC/dsPIC, MicroBlaze and Nios II. Everything ships inside the platform; there is nothing for you to install.
The control-flow graph engine contributes static call-path evidence. Review it alongside runtime observations, configuration and coverage before drawing a vulnerability-specific conclusion or publishing a VEX statement.
19
CPU architectures
35
Firmware and filesystem formats
60
Security test cases
385K+
CVE records in FDIE's NVD mirror
What is in-house and what is not
FirmBin, extraction, binary parsing and CVE matching are ours and do not depend on Ghidra, Capstone, radare2 or binwalk. Runtime emulation uses QEMU and Unicorn; malware scanning uses YARA. All of it is bundled, and listed on the Security page.
Connect technical findings to assessment requirements.
FDIE maps assessed evidence to eleven compliance frameworks and makes coverage gaps visible, helping your team prepare a documented product assessment.
Consumer IoT security baseline
European baseline covering credential management, software updates, secure communications and more.
Radio Equipment Directive
Harmonised standards for network security, privacy and monetary-value protection under RED Article 3.3, applying from August 2025.
Firmware security testing
A methodology for firmware security testing. FDIE contributes supported automated checks and evidence alongside manual assessment.
Platform firmware resilience
Guidelines for platform firmware protection, detection and recovery.
IoT device cybersecurity
A core baseline for IoT device cybersecurity capabilities.
Industrial cybersecurity
Component-level requirements for industrial automation and control systems, with applicability determined for the product and its intended use.
Health software lifecycle
Security activities across the health-software lifecycle; used to structure applicable lifecycle activities.
US medical device premarket
Cybersecurity requirements for cyber devices in FDA premarket submissions, statutory since March 2023.
India consumer IoT
The Telecommunication Engineering Centre code of practice for securing consumer IoT, Release 2.0.
EU Cyber Resilience Act
Article 14 reporting obligations apply from September 2026 within the regulation’s scope. FDIE records the assessment and submission references; it does not issue a conformity grade.
Founder-led, built from firsthand experience.
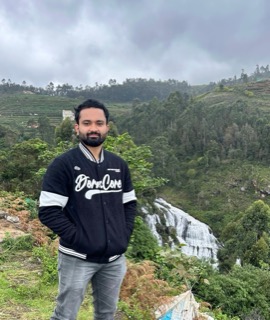
FDIE was founded by Manish Sharma. Before this, he spent years on the other side of the audit table: chasing CVEs in vendor SDKs, building SBOMs by hand the night before a deadline, and starting from zero on every new firmware version. FDIE is the tool he wished he had, so he built it.
Founder and Chief Executive Officer
A cybersecurity background spanning application security, vulnerability research and offensive security, with binary analysis and firmware security as a deeper specialisation. Built FDIE and the FirmBin disassembly engine from the ground up, with correctness as the starting point.
LinkedInSmall and founder-led, for now.
We are not hiring yet. When firmware, embedded security or compliance tooling roles open, they appear on the careers page first.
Founded
West Bengal, India
Entity
Registered company, India
Status
Access arranged by our team, 21-day free trial on the full platform.
Start with one product and two releases.
Review a sample comparison with us. Then scope a supported image pair, hosting requirements and the evidence your team needs to evaluate.
21-day free trial on the full platform. No card, no automatic conversion.